Early in our careers, most of us are rewarded for being responsible. We build the system. We fix the outage. We make it work. That competence gets noticed and often becomes the reason we are promoted.
At some point, though, responsibility turns into accountability, and that transition is rarely discussed out loud.
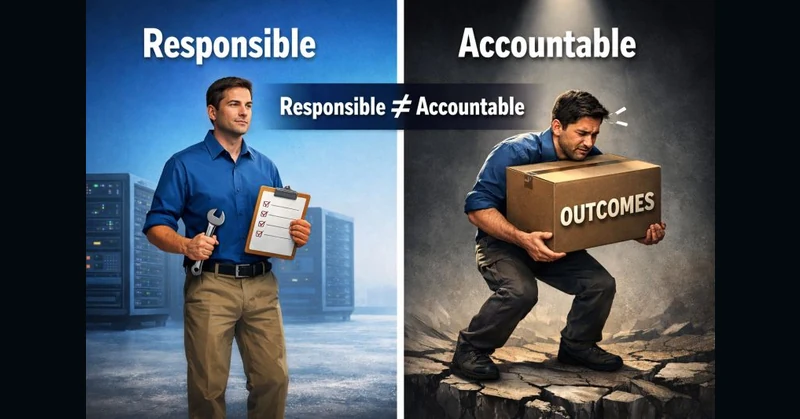
Being responsible means you do the work. Being accountable means you own the outcome. Those two ideas sound similar, but in practice they are very different.
In IT leadership, the real tension appears when accountability is assigned without authority. There is no control over vendor selection, limited influence over budget, and little say in staffing or long-term operations. Yet when the system fails, users are unhappy, or risk surfaces, IT is expected to explain and absorb the impact.
That is not leadership alignment. That is exposure.
One of the most important questions an IT leader can ask early in any project is simple: who is accountable for this after go-live? Not who installs it. Not who supports it day to day. Who owns the outcome six months later.
When that question has no clear answer, the organization is quietly transferring risk, usually to IT, without realizing the long-term cost. Over time, this blurring of responsibility and accountability increases burnout, slows innovation, and erodes trust. People stop taking smart risks because they know they will own the consequences without the authority to shape them.
Strong organizations are intentional about drawing this line. Struggling ones avoid the conversation until something breaks.
I am curious how others handle this.
Have you been held accountable for outcomes you did not have authority over? How does your organization define ownership after go-live? What questions do you ask to protect your teams from inherited risk?